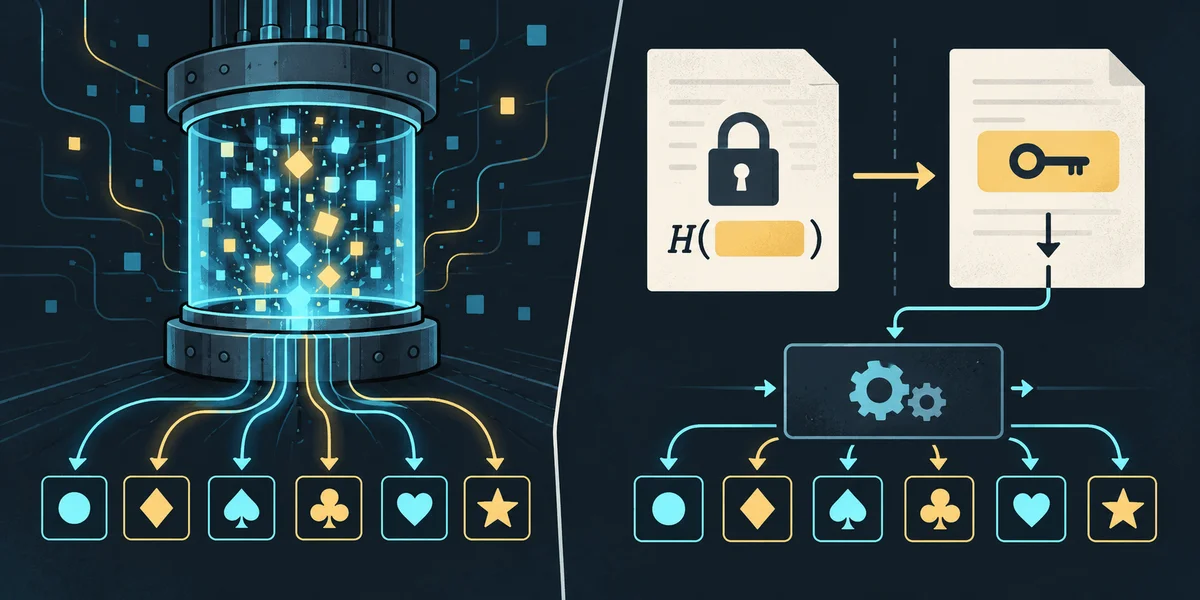


Random generation and Provably Fair answer different questions. An RNG supplies values used by a game; a commitment-and-reveal workflow can let a player check that a recorded round agrees with earlier published data and a specified calculation. The two can coexist. Neither a testing logo nor a matching hash alone establishes every claim about a casino. A useful comparison states exactly what was checked, when the evidence became available and which part remains outside that check.
Generation, mapping and settlement
Separate three layers. First, a process generates seeds or random inputs. Second, a documented mapping converts those inputs into cards, symbols or a multiplier. Third, an accepted wager settles under its rules. A statistical test of outcomes concerns a defined distribution and dataset. A cryptographic comparison concerns specific bytes and records. A correct multiplier calculation does not automatically show that the player's requested target was accepted, the correct amount was credited or a withdrawal arrived.
The name of an algorithm does not identify the deployed generator, entropy quality or configuration. We do not establish that a casino uses MT19937, thermal noise, a quantum source or a certified hardware device. Statistical plausibility and unpredictability are separate properties. Passing a collection of tests is not a proof of every future outcome, while a weak secret can remain guessable despite being hashed. Evaluate implementation evidence rather than assuming an impressive algorithm name settles those questions.
What conventional oversight can include
As a jurisdiction-specific example, the British Gambling Commission's procedure covers source review, raw and mapped outputs, game maths and applicable changes before release. Its annual audit also examines change controls. This is broader than a universal snapshot once every 12 to 24 months. These are requirements for the relevant licensed activities, not evidence that a particular partner, deployment or game here passed them. We have not inspected a live operator's private test report or current register entry.
The Commission's separate live RTP guidance requires monitoring for underpayments and overpayments, with volume and volatility considered and aggregation that does not conceal channel errors. A player normally cannot reproduce that entire backend process. That limitation is different from asserting that no ongoing controls exist. A certificate has an entity, software version, scope and date; a displayed badge alone does not establish them. Use the actual record to assess the specific claim rather than treating a logo as complete proof or as worthless.
What a commitment adds
In a suitable workflow, the operator publishes a commitment before the relevant input or wager boundary, later reveals the committed data, and supplies enough information to reproduce the mapping. Hashing the revealed bytes and comparing them with the earlier commitment tests one link. Under the relevant cryptographic assumptions, changing committed data while keeping the same recorded hash should be computationally difficult. That is not an absolute statement that fraud is physically impossible or that every field in the interface is truthful.
The commitment needs an identifiable round and reliable earlier record. A hash shown only after the outcome does not establish prior commitment. A copied screenshot without chronology may also leave that issue unresolved. Protocols differ in which inputs are committed, when clients contribute, when seeds rotate and when secrets become available. We do not supply a universal five-second schedule, a universal nonce or an algorithm for every crash game. Verification may occur after reveal rather than while the flight is still live.
Why client input does not prove unbiased selection
A client seed can constrain an operator's choices only in the actual timing and threat model. If that seed is already known before the operator chooses its own seed, the operator can evaluate candidates before publishing a commitment. Each later commitment comparison can still match. This possibility does not break the hash function and does not accuse a named provider of doing it. It shows why “a client seed exists” alone cannot prove that candidate selection was unbiased.
Unpredictable independent input fixed after an operator's binding commitment can change that threat model. Complete rules must still address input influence, reuse, selective aborts, missing rounds and mapping. A nonce is often an index or counter; it is not automatically independent secret entropy. Repeated or predictable inputs need the protocol's actual analysis. A claim of seed integrity should say whether it means consistent disclosure, unique use or evidence about the process that chose the seed.
| Check | What a match supports | What remains outside it |
|---|---|---|
| Prior commitment | Revealed bytes agree with the retained record | Unbiased choice before commitment |
| Mapped round result | Inputs reproduce the recorded result under this mapping | Licence, accepted wager and custody |
| Accepted wager ledger | Gross and net reconcile with recorded movements | Future withdrawals or solvency |
| Statistical test | Evidence under its dataset and null model | Every individual or future event |
| Certificate record | Stated entity, scope and version as recorded | Every deployment and market |
A matching seed can accompany a false multiplier
Consider the explicitly educational HMAC model below. It uses UTF-8 text, HMAC-SHA256(server, client:nonce), the first 13 hexadecimal digits, a cent-floor reciprocal mapping and no divisibility rule. It is not an official Lucky Jet or Stake verifier and does not implement Aviator's separate SHA-512 path. With the supplied synthetic inputs it calculates 1.45x. The same seed commitment still matches if a record falsely claims 2.00x; the result comparison catches the discrepancy.
This is why the claim “any false displayed result must change the seed hash” is incorrect. Check commitment and outcome separately. A missing expected outcome should produce “not compared”, not a green match. A different mapping or input encoding can also cause a discrepancy without establishing its cause. Retain the full inputs, version and original record before concluding which component was wrong. No single discrepancy here automatically revokes a licence or proves malicious intent.
| Claimed outcome | Calculated outcome | Seed commitment | Outcome check |
|---|---|---|---|
| 1.45x | 1.45x | matches | matches |
| 2.00x | 1.45x | matches | mismatch |
| absent | 1.45x | matches | not compared |
Reproduce the comparison
The following Python 3 example needs only the standard library. The synthetic vector was independently checked against our existing JavaScript BigInt reference. No private seed, casino login, wager or API request is involved. The commitment value is an expected earlier record for the illustration; it is not evidence of an actual historical publication. The two claimed outcomes deliberately show the difference between calculation, commitment comparison and outcome comparison.
import hashlib
import hmac
import json
import logging

server = "crashmath_demo_server"
client = "crashmath_demo_client"
nonce = 2
prior_commitment = (
    "da780fd3750c0f33a24c9db836f254463f96ca06f95e17f46b54900a442d25f7")
commitment = hashlib.sha256(server.encode("utf-8")).hexdigest()
digest = hmac.new(server.encode("utf-8"),
    f"{client}:{nonce}".encode("utf-8"), hashlib.sha256).hexdigest()
integer = int(digest[:13],16)
grid = 2**52
cents = max(100,97*grid//(grid-integer))
assert cents == 145
checks = []
for claimed_cents in (145,200,None):
    checks.append({"claimedCents":claimed_cents,
        "calculatedCents":cents,
        "commitMatches":commitment == prior_commitment,
        "outcomeStatus": "not-compared" if claimed_cents is None
            else "match" if claimed_cents == cents else "mismatch"})
logging.basicConfig(level=logging.INFO,format="%(message)s")
logging.info(json.dumps({"commitment":commitment,"digest":digest,
                         "checks":checks}))
Different protocols stay different
Aviator, a provider's HMAC crash implementation and a slot verification workflow can have different inputs and transformations. Do not substitute one formula because all use a fairness label. BGaming, for example, publishes its own slot workflow; verification is not confined to crash games. Preserve exact byte encoding, separators, input order, nonce policy, digest selection, rounding and any instant-result rule of the selected version. A shortened hash for display cannot replace the full value needed for a comparison.
Verification also does not require a blockchain in every design. A conventional hash commitment can be exchanged without a chain transaction. Whether a particular product uses a public ledger is a separate fact to establish, including what that ledger actually records. A chain entry does not by itself identify the authorised game rules, prove the selection distribution or establish custody of a player's balance. Likewise, using no blockchain does not prevent a well-defined per-round consistency check.
RTP, licensing and account funds remain separate
A reproducible negative-edge mapping can be internally consistent and still have a house advantage. Conversely, a disclosed edge does not prove that all data needed to reproduce each settlement were supplied. A game supplier's licence, an operator's permission to serve a market and the player's eligibility are distinct records. We do not certify those records from a fairness label or attach a universal regulatory status to a mathematical formula. Check the relevant entity, domain, activity and current jurisdictional record when that decision matters.
Per-round consistency does not establish availability of withdrawals, solvency, ownership of account funds, bonus eligibility or support quality. It also does not guarantee relief from anxiety or prevent changes in stakes after a loss. You can value the additional evidence without turning it into a promise of complete trustlessness or a behavioural treatment. The practical benefit is narrower and useful: a particular recorded calculation can be checked by someone other than the party that displayed it.
Follow the evidence in order
Identify the exact game and version, obtain the documented protocol, retain the prior commitment with its round and chronology, and collect the disclosed inputs after reveal. Recompute each stage, compare the earlier hash and recorded outcome, then reconcile the accepted wager's gross payout and account movements. Record each stage as matched, mismatched or unavailable. If the reveal is not yet due, say pending. Several sampled matches do not establish the entire unsampled history, independent seed choice or future performance.
The EV calculator and verification examples are optional. Direct partner registration is available without a mandatory demo, calculation or test wager. Use the extra evidence for the question it actually answers; do not turn verification into a required purchase of more rounds.
British primary sources, checked 23 October 2026: RNG requirements RTS 7 (updated 7 May 2024), testing procedure (13 September 2024), annual audit (29 June 2022), live RTP monitoring (7 December 2023), BGaming’s own verification workflow.