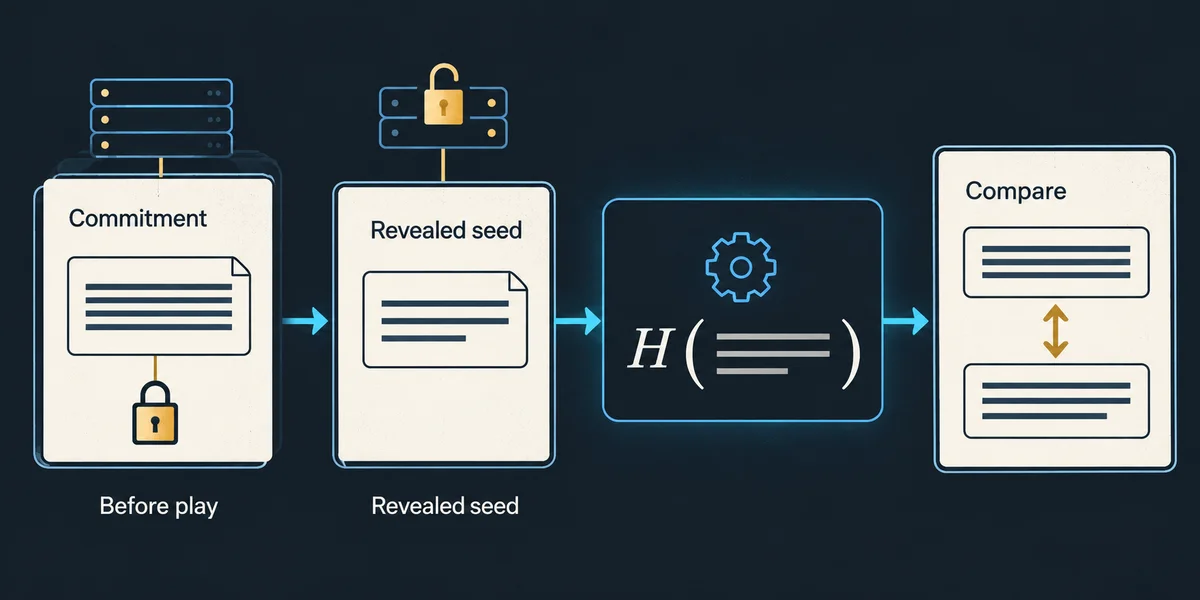


Provably fair methods let a reader check particular relationships between a recorded commitment, revealed inputs and a game result. A successful check has a defined scope. It does not remove every need to trust an operator, prove that funds can be withdrawn or make a negative-expectation wager profitable. This guide separates commitment checking from result reproduction, distinguishes provider protocols and supplies one explicitly educational calculation. The example is not an official Lucky Jet, Stake or Aviator verifier, and the current browser tool reports a calculated result rather than an automatic certificate.
1. Three records are needed for three different questions
First ask what was fixed before the relevant wager. A common commitment is a hash of a server seed. Preserve that value with a round or seed-pair identifier and evidence of when it was available. After the seed is revealed, hashing it according to the same encoding can show whether it matches the recorded commitment. If both values are collected only after play, their agreement does not establish that the commitment existed before the bet. Timing is part of the evidence, not something the hash can reconstruct.
Next ask whether the revealed inputs reproduce the displayed outcome under the exact game's rules. This needs the input order, separators, character encoding, hash or keyed-hash construction, numeric conversion, rounding and any special conditions. A server seed can match its commitment while a displayed multiplier does not match the calculation. Conversely, a result can be reproduced without proving a prior commitment. These are separate comparisons and should be recorded separately.
Finally, distinguish the result from settlement. Whether a wager was accepted, when an automatic target applied, what stake was returned and whether a withdrawal occurred require additional records. A round hash contains no bank-transfer confirmation. Checking a seed relationship is useful evidence about that relationship; it cannot independently certify every screen, payment rule or account action surrounding the round.
2. Choose a protocol before entering inputs
A name containing provably fair does not define a universal formula. The relevant provider documentation and installed version determine which inputs are required. A generic form asking for a server seed, client seed and nonce can be appropriate for one model and wrong for another. Do not add a nonce, colon or divisibility rule merely because an unrelated calculator uses one. Missing documentation should remain an unresolved limitation, not be filled with a familiar algorithm.
| Scope | Input construction | Limit |
|---|---|---|
| Educational CSV | HMAC(server,client:nonce) | No extra divisibility rule |
| CrashMath Aviator branch | SHA-512(server+c1+c2+c3) | No nonce; selected-version evidence still needed |
| Stake general byte generator | HMAC with nonce and cursor | Not a universal Crash multiplier mapping |
SPRIBE describes SHA-512 seed combination and a SHA-256 next-server commitment, with game-specific conversion. Stake publishes a general HMAC byte generator with nonce and cursor. Neither description makes the educational formula below the exact algorithm of every Crash installation.
CrashMath keeps a separate Aviator path: SHA-512 of the server seed followed by three client strings, without separators or a nonce, and its declared multiplier mapping. That accepted calculation is not replaced here. A real-round assessment still needs the matching version and recorded inputs. The HMAC examples labelled with Lucky Jet or Stake context are illustrative models, not authenticated provider specifications.
3. A hash, HMAC and encryption are different operations
A hash maps input bytes to a digest. A SHA-256 digest is normally displayed as 64 hexadecimal characters; that display is not an encrypted server seed with a decryption password. HMAC combines a secret key and message using a hash construction. As RFC 2104 defines it, HMAC is message authentication using a shared secret, not an asymmetric public/private key pair. Publishing a hash is also not automatically a zero-knowledge proof.
Cryptographic resistance is a security assumption with conditions, not a statement that two different inputs can never share a finite digest. A weak seed drawn from a small predictable set can be guessed without searching every possible 256-bit string. A commitment alone does not measure seed entropy. The party generating a seed may know it already; a player contributing a client string does not automatically make it unpredictable to that party at the necessary time.
Changing an input changes what is being calculated. It does not guarantee a distinct displayed multiplier: the conversion deliberately maps many digest values to the same rounded amount. Likewise, a changing nonce is an input convention, not a proof of independence or a substitute for bet authentication. Exact security conclusions require the protocol and implementation, not just the name of a hash function.
4. One declared model, with correct numeric units
For instruction, take HMAC-SHA256 with the UTF-8 server string as key and the UTF-8 message clientSeed:nonce. Interpret the first 13 hex characters as integer I. There are N=2^52=4,503,599,627,370,496 possible integers from zero to N-1. Set u=I/N. This is a finite grid in [0,1), not a continuous random variable. Treating the digest slice as uniform is a model assumption; the arithmetic alone does not prove that property for a real data source.
Use edge E=0.03 as a fraction. The displayed model multiplier is max(1, floor(100(1-E)/(1-u))/100). Equivalently, its integer cents are max(100, floor(97N/(N-I))). Do not subtract 0.03 from 100: 100(1-0.03) equals 97. The model has no extra modulo-33 or modulo-101 rule. Adding one would change the distribution and the return. Our public synthetic CSV follows this no-modulo model.
| Integer I | Model multiplier |
|---|---|
| 0 | 1.00x |
| 1 | 1.00x |
| 2251799813685248 | 1.94x |
| 2150338892260083 | 1.85x |
For the hex segment 7a3b8c9d1e2f3, I is 2,150,338,892,260,083 and u is approximately 0.4774711497868196, yielding 1.85x. The displayed 1.00x outcome includes every grid point with I<4N/101. Its exact count is 178,360,381,282,000, approximately 3.960396% of the grid. It is not simply a 3% atom. A special boundary rule for a wager at exactly 1x would also need to be stated rather than inferred.
In the ideal reciprocal approximation, targets k above 1 have hit probability (1-E)/k and expected net result -E per unit wager. Finite-grid rounding and allowed target precision need attention for exact calculations. This expectation describes a specified model, not a measured RTP of a named operator or a guaranteed loss on every session. A lower target changes variance and hit frequency; it does not by itself create positive expectation.
5. Reproduce a complete synthetic example
Download illustrative_crash.mjs and run it with Node.js. It uses built-in cryptographic functions and integer arithmetic, without external packages. Its default inputs are the public strings below. They are test data, not captured live seeds. The code returns status calculated, the seed hash, round hash and multiplier. It does not return isValid=true or silently invent an expected result.
{
  "serverSeed": "crashmath_demo_server",
  "clientSeed": "crashmath_demo_client",
  "nonce": 2,
  "status": "calculated",
  "model": "HMAC-SHA256, 3% reciprocal, cent floor, no divisibility rule",
  "commitment": "da780fd3750c0f33a24c9db836f254463f96ca06f95e17f46b54900a442d25f7",
  "roundHash": "55b8a44e6e1065c9fa7e86f9c7a073df271ba21b6307bb029cf4961ea6bb6be5",
  "integer": "1508024303149318",
  "multiplier": "1.45"
}
Both seeds are used as literal UTF-8 text. A string that looks hexadecimal is not decoded into bytes in this example. Whitespace, case, Unicode characters, separators and nonce formatting affect the message. The helper rejects an empty seed or a nonce that is negative, fractional or outside the safe integer range. It does not trim or normalise a supplied seed behind the reader's back. These choices are part of its declared educational specification.
The downloadable example and the browser hash walkthrough serve different declared models. The browser HMAC modes include additional divisibility conditions and are labelled accordingly. Do not expect equal multipliers across different mappings just because the same digest appears. Select the intended model first, then compare the steps that model actually specifies.
6. A comparison needs an independently recorded expected value
To check a real commitment, compare the calculated seed hash with the value recorded before play for that exact round or seed pair. To check a result, compare the calculated multiplier with the recorded result under the documented formatting rules. If a relevant input is missing, the correct status is not checked or insufficient evidence. Calculating a value and comparing it with itself is not verification.
The current browser tool does not accept a separate expected commitment and recorded multiplier for automatic comparison. Its result is therefore calculated. Where the protocol is appropriate, the reader must perform and document the independent comparison. The example code below illustrates explicit comparisons for known synthetic expected values. Agreement in this fixture does not prove that any casino published a commitment at the required time.
import { calculateIllustrative } from './illustrative_crash.mjs';
const calculated = calculateIllustrative('crashmath_demo_server', 'crashmath_demo_client', 2);
// Synthetic expected values only; no real pre-round timing is established.
const expectedCommitment = 'da780fd3750c0f33a24c9db836f254463f96ca06f95e17f46b54900a442d25f7';
const expectedMultiplier = '1.45';
console.log({
  commitmentMatches: calculated.commitment === expectedCommitment,
  resultMatches: calculated.multiplier === expectedMultiplier
});
A mismatch needs investigation. Check the version, selected round, encoding, seed order, nonce, cursor, rounding and transcription. Preserve the original record rather than editing it to make a match. A persistent unexplained discrepancy is evidence of a discrepancy; it does not by itself identify fraud, a particular responsible party or a payment outcome. Successful reproduction also does not rule out every other failure mode.
7. What the method does not settle
Commitment matching does not show that the seed was sampled uniformly, that the operator could not select among candidates before committing or that all eligible rounds were retained. Client contribution can help only under the relevant timing, unpredictability and acceptance conditions. A known client seed is not a universal defence against preselection. The protocol must explain what each party knows and when, including any ability to reject or restart a round.
A gap in a nonce sequence is not automatic cryptographic proof of discarded losses. The documented scope may include other wagers, different games or a reset. Nor does an uninterrupted counter prove that no rounds were omitted from a separate display. Record the scope before interpreting gaps. A hash chain similarly requires a specified direction, anchor, length and timing; no universal chain size is assumed here.
Using browser cryptography also does not certify the privacy of an entire page. Analytics, third-party scripts and network behaviour are separate implementation questions. Do not paste unrevealed active secrets into an unfamiliar service. Use disclosed historical test data or an inspected local calculation where appropriate. There is no quantum-security timetable, laboratory certificate or blanket operator approval implied by this guide.
8. Keep the practical check bounded
Record the game and version, retain the prior commitment if available, copy all revealed round inputs exactly and obtain the complete conversion rule. Reproduce the commitment and outcome separately, noting which comparisons could actually be made. Keep settlement records separate from the mathematical calculation. If the rule is unavailable, state that limit instead of substituting another game's formula.
The EV calculator can then explore an explicitly chosen edge; it does not authenticate a game. Direct partner registration on this site is a separate commercial action and requires no completed verification exercise. A successful calculation is useful technical evidence within its scope. It is not a reason to increase a stake or assume future profits.